Anthropic’s latest AI Model, Claude Mythos, will break the cybersecurity vulnerability management operational models. Mythos is so good at discovering and building viable exploits it is currently being rolled-out in a controlled manner under “Project Glasswing“. Those cybersecurity companies who have early access are attesting to the blazing speed and accuracy of the model and have declared the traditional processes the industry uses to manage vulnerabilities in their systems is no longer viable.
The Problem is Twofold
First, new AI models like Mythos, are incredibly proficient at identifying weaknesses in code that could be leveraged by cyber attackers. Mythos has found over 2000 high-severity vulnerabilities, including in every major operating system and web browser!
The second issue is how fast workable exploits can be created to take advantages of discovered vulnerabilities. The latest AI models are highly proficient and quickly figuring out how to leverage weakness and chain them together across multiple vulnerabilities to gain unprecedented access to targeted systems and infrastructures.
The speed of discovery and exploitation of vulnerabilities is now well beyond what defenders can address. Currently, the industry must become aware of vulnerabilities through industry announcements, direct notification by researchers, or in rare cases by self-discovery efforts. They must then verify the vulnerability and understand its potential applicability to their environment. It gets rated and based upon that rating; resources will be committed to develop a patch. The patch must be tested and then scheduled for roll-out in a way that it can be withdrawn if something unforeseen occurs.
This takes time and may incur downtime for impacted systems.
Legacy Patching Fails
Most organizations have a cadence for addressing different severity vulnerabilities. A patch calendar may bundle fixes to control the disruption and prioritize the most urgent fixes. High risk may be fixed in weeks or a month, medium in several months, and low, perhaps every year if they choose to fix them at all.
The goal is simply to fix the vulnerabilities before the attackers could create and deploy an exploit in the wild, which typically took months.
No longer.
Now, what took months will take minutes with Mythos and other AI models.
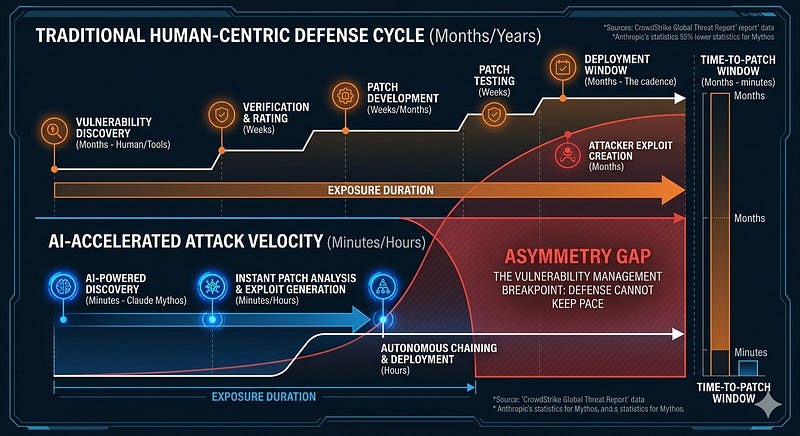
That breaks the entire vulnerability management system that protects our digital world.
For those who read my annual cybersecurity predictions (video version), we can check off prediction number 2, which outlined how AI acceleration would shrink the time-to-patch window dramatically, beyond what is currently possible for cybersecurity teams.
Predicting Strategic Outcomes
First, organizations will cut corners to speed up patch release for the impactful vulnerabilities most likely to be exploited. This will shrink the patch window a little, but not enough, and introduce errors in patches which will have undesired impacts on users. Essentially, the number of ‘bad patches’ will increase.
Secondly, the increased attack velocity will drive software developers to commit much more to using AI tools to proactively detect and resolve vulnerabilities prior to product release. This should have happened long ago, but in the race to market, security vetting often gets deferred to later. The outcome will be slower product release timelines from responsible vendors. The haphazard companies will want to take advantage and continue to push vulnerable code to get into the market faster. But that will eventually have consequences.
Third, there will be massive shift for cybersecurity teams to adopt these AI tools to compete with attackers by trying to detect and address vulnerabilities before the hackers. The tools, processes, and operating models will need to be entirely redrawn. The window of exposure will be the metric that must shrink, from months to hours.
Adaptation Required
The latest AI tools will compress the vulnerability lifecycle from discovery to exploitation at a pace that challenges the foundations of today’s security operations. Organizations that continue to rely on legacy processes will find themselves operating outside the window of safety. Defenders can no longer rely on traditional disclosure cycles, patch cadences, or reactive security models when intelligent systems can discover and weaponize weaknesses in hours. To survive this new era, organizations must reinvent their processes around AI-driven velocity. The signals are clear; it is time to radically adapt vulnerability management or be victimized.


Comments
Much required topic to be discussed. Excellent timely post !