Deploying industry-specific IT eliminates workflow bottlenecks and protects your revenue by aligning technology infrastructure directly with your daily operational realities. Every minute your systems fail to support your proprietary workflows, you l
Search Results (735)
What a Business Logic Vulnerability Actually Is
A business logic vulnerability is a flaw in the rules and assumptions that govern how an application is supposed to be used, not a flaw in how it parses input. The request that exploits it is syntactica
Member Contribution - Weekly CISO Podcast Pick
This Week's Pick by David B. Cross (CISO, Atlassian)
Series curated by the CISO Platform community, sharing practical security leadership resources recommended by experienced CISOs and senior practitioners
New York, USA. Techanic Infotech says that user privacy is very important for dating applications. It is not a feature but a core part of these applications. As users find out more about how their data's collected, stored and used they want the compa
In an age where AI-driven agents increasingly handle sensitive requests, the critical question is: how do we trust the identity behind every interaction? Traditional methods like passwords and OTPs are proving inadequate in stopping fraud, deepfakes,
Selecting the right attack surface management vendor is essential for safeguarding sensitive data and securing your organization against vulnerabilities. Attack surface management involves identifying and mitigating risks across your digital footprin
CISO burnout is a serious issue and through this discussion, we try to find out the impact of this issue on organizations and individuals. The CISO role is operation intensive and gruelling. In most cases CISOs remain in an organisation for about 1 t
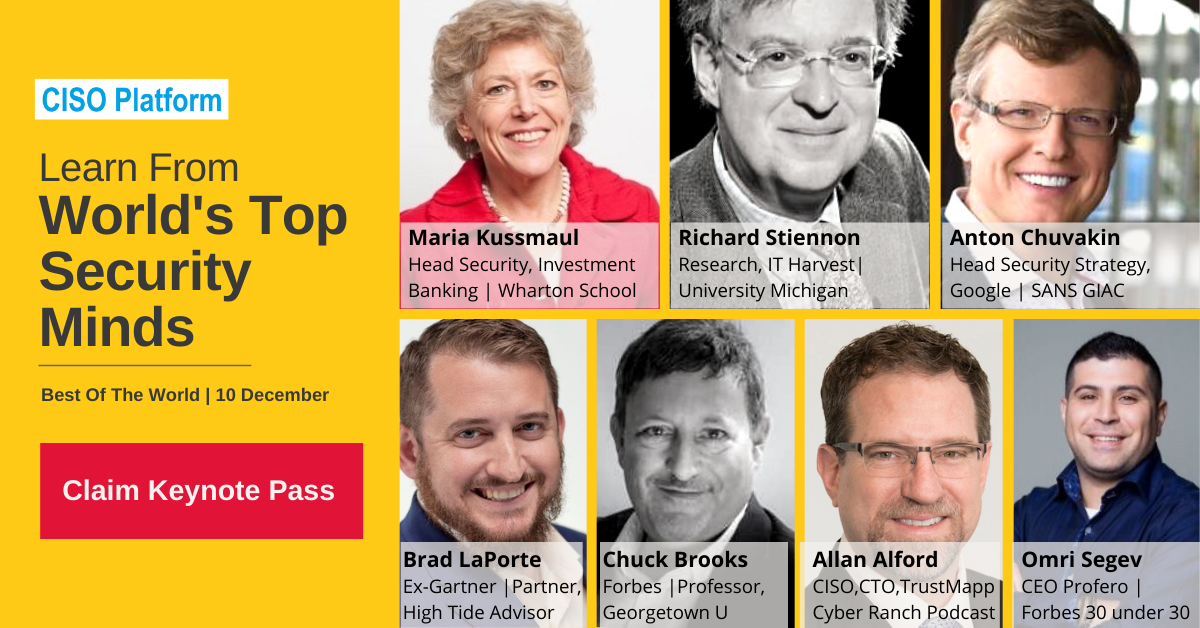
Keynotes From World-Renowned Industry Experts (Best Of The World) :
- "The state of security markets and changing buying priorities" by Maria Kussmaul - Head Security, Investment Banking | Wharton School
- "Q3 2021 Changes To The Entire IT Secur
[Posted on Behalf of Steve King, Director, Cybersecurity Advisory Services Information Security Media Group (ISMG) ]
Many cybersecurity analysts have warned of the rapidly emerging threat from an expanded IoT space. And as you have noticed, it appea
[Posted on behalf of Gary Hayslip CISO Softbank Investment advisor] (Source)
I recently published on LinkedIn an article about the foundational elements of the CISO role that will not change as it rises to meet the challenges of COVID-19 on busines
We all understand the significance of cloud when it comes to economies of scale, reduced time to market, operational effectiveness and ease with which you can deploy applications to it and most of us are good in leveraging those benefits too. But how
You've got Mail!
While the world continues to battle with the Corona pandemic, there is another pandemic unfolding in digital space. Businesses and people are seeing an unprecedented onslaught of cyberattacks. As organisations try to maintain the busi
These days’ web applications are under siege. Commercially motivated Hackers, bots, and fraudsters are attacking around the clock, attempting to steal data, disrupt access, and commit fraud which today’s next generation firewall, IPS and other networ
A generic definition of a crime would be an act that is in violation of the applicable laws. A crime / criminal offense may essentially hurt an individual or the community (city or a nation) at large. This concept has now been taken to the next level
Saurabh Kaushik,Sr Manager Information Security, Lupin Pharma, talks to CISO Platform on the biggest drivers and barriers of IAM adoption and the top challenges a CISO/organization can face while adopting IAM.
How important is IAM? Why should organiz
Join The Community Discussion

CISO Platform
A global community of 6K+ Senior IT Security executives and 40K+ subscribers with the vision of meaningful collaboration, knowledge, and intelligence sharing to fight the growing cyber security threats.
Join CISO Community Share Your Knowledge (Post A Blog)

